

Introducing Envoy Visitors Critical: A new standard in visitor security


Today we’re introducing Visitors Critical, a new offering built for organizations with the highest bar for security and compliance. In many ways, it’s a natural next step. For years we’ve worked alongside customers in defense, advanced manufacturing, AI, and critical infrastructure. Visitors Critical brings everything we’ve learned into one dedicated solution for high-consequence environments.
For these facilities, a single security gap can end in stolen IP1 or lost goods2, expose controlled technology, trigger ITAR penalties that can run into the millions3, or jeopardize CMMC compliance and the government contracts that depend on it4. And in facilities where the work itself is hazardous, the stakes aren’t only financial — the wrong person in the wrong place can mean a serious health and safety incident5.
Over the past several months, our team has been on the ground where these decisions happen: in guard shacks as unscheduled trucks idle at the gate, at front desks juggling lobbies full of contractors, and in the security operations centers (SOCs) that watch over them. We’ve also consulted closely with cybersecurity experts along the way. From that work and deep collaboration with our Customer Advisory Board, we know it’s a constant race against an evolving threat landscape: forged IDs that AI makes harder to spot, approval processes that get stuck in error-prone email threads, unvetted contractors showing up with expired credentials on file, security policies that drift from site to site, and rules enforced only as consistently as the person at the front desk that day. That’s why we built Visitors Critical.
Visitors Critical brings identity, documents, screening, approval workflows, and access management into one governed system where every decision and action is auditable. Built to scale across complex organizations and every facility they operate, it orchestrates the people, teams, and data behind every visit, routing each review and escalation to the right owner. The result is operations that are both more secure and more efficient. We built Visitors Critical based on a few core beliefs:
Our core product principles:
- From identity to access
- A layered approach to risk and compliance
- Tailored to your industry
- Sensitive data should be need-to-know
- Ease of use drives adoption, and adoption is security
From identity to access
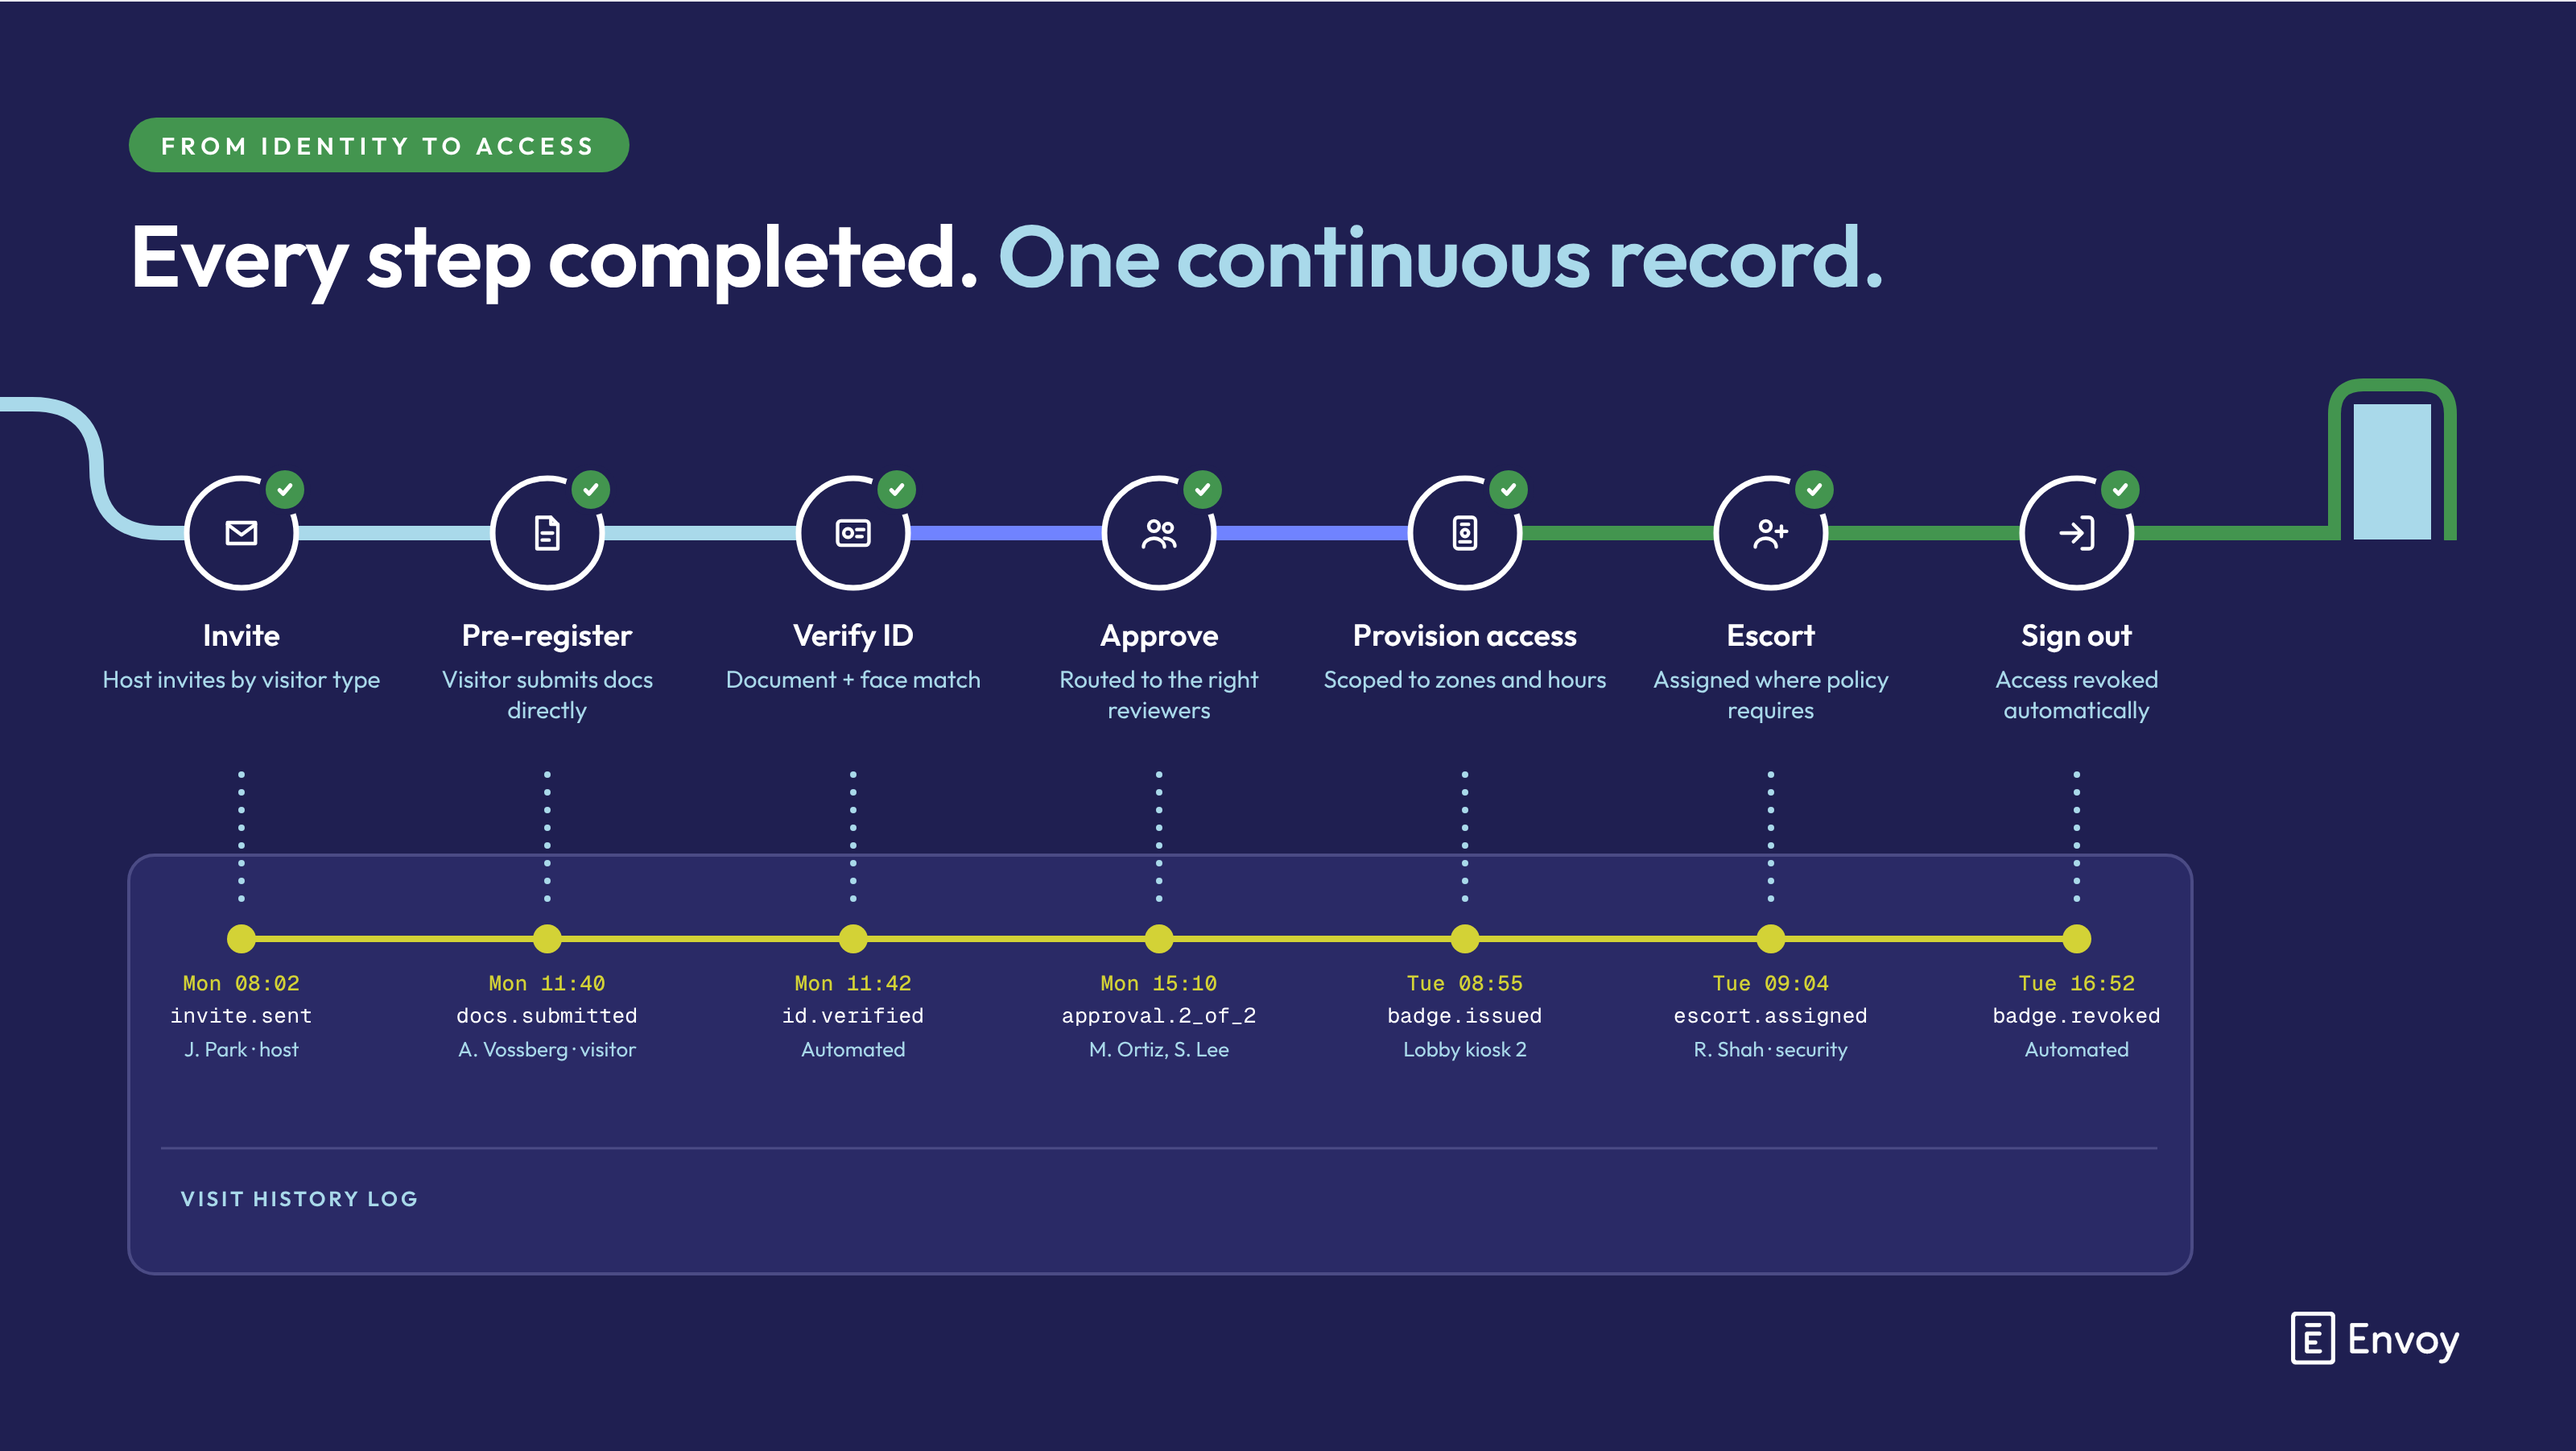
Most visitor incidents happen in the gaps between systems: approvals over email, badges provisioned in a separate system, documents stored in a shared drive. Visitors Critical governs the full lifecycle in one system of record: invitation, pre-registration, identity verification, approvals, access provisioning, escort requirements, and sign-out, with a detailed audit trail at every step. And because Envoy is a global system of record, policies apply at every site, enforced by the system rather than by whoever is at the desk that day.
A layered approach to risk and compliance
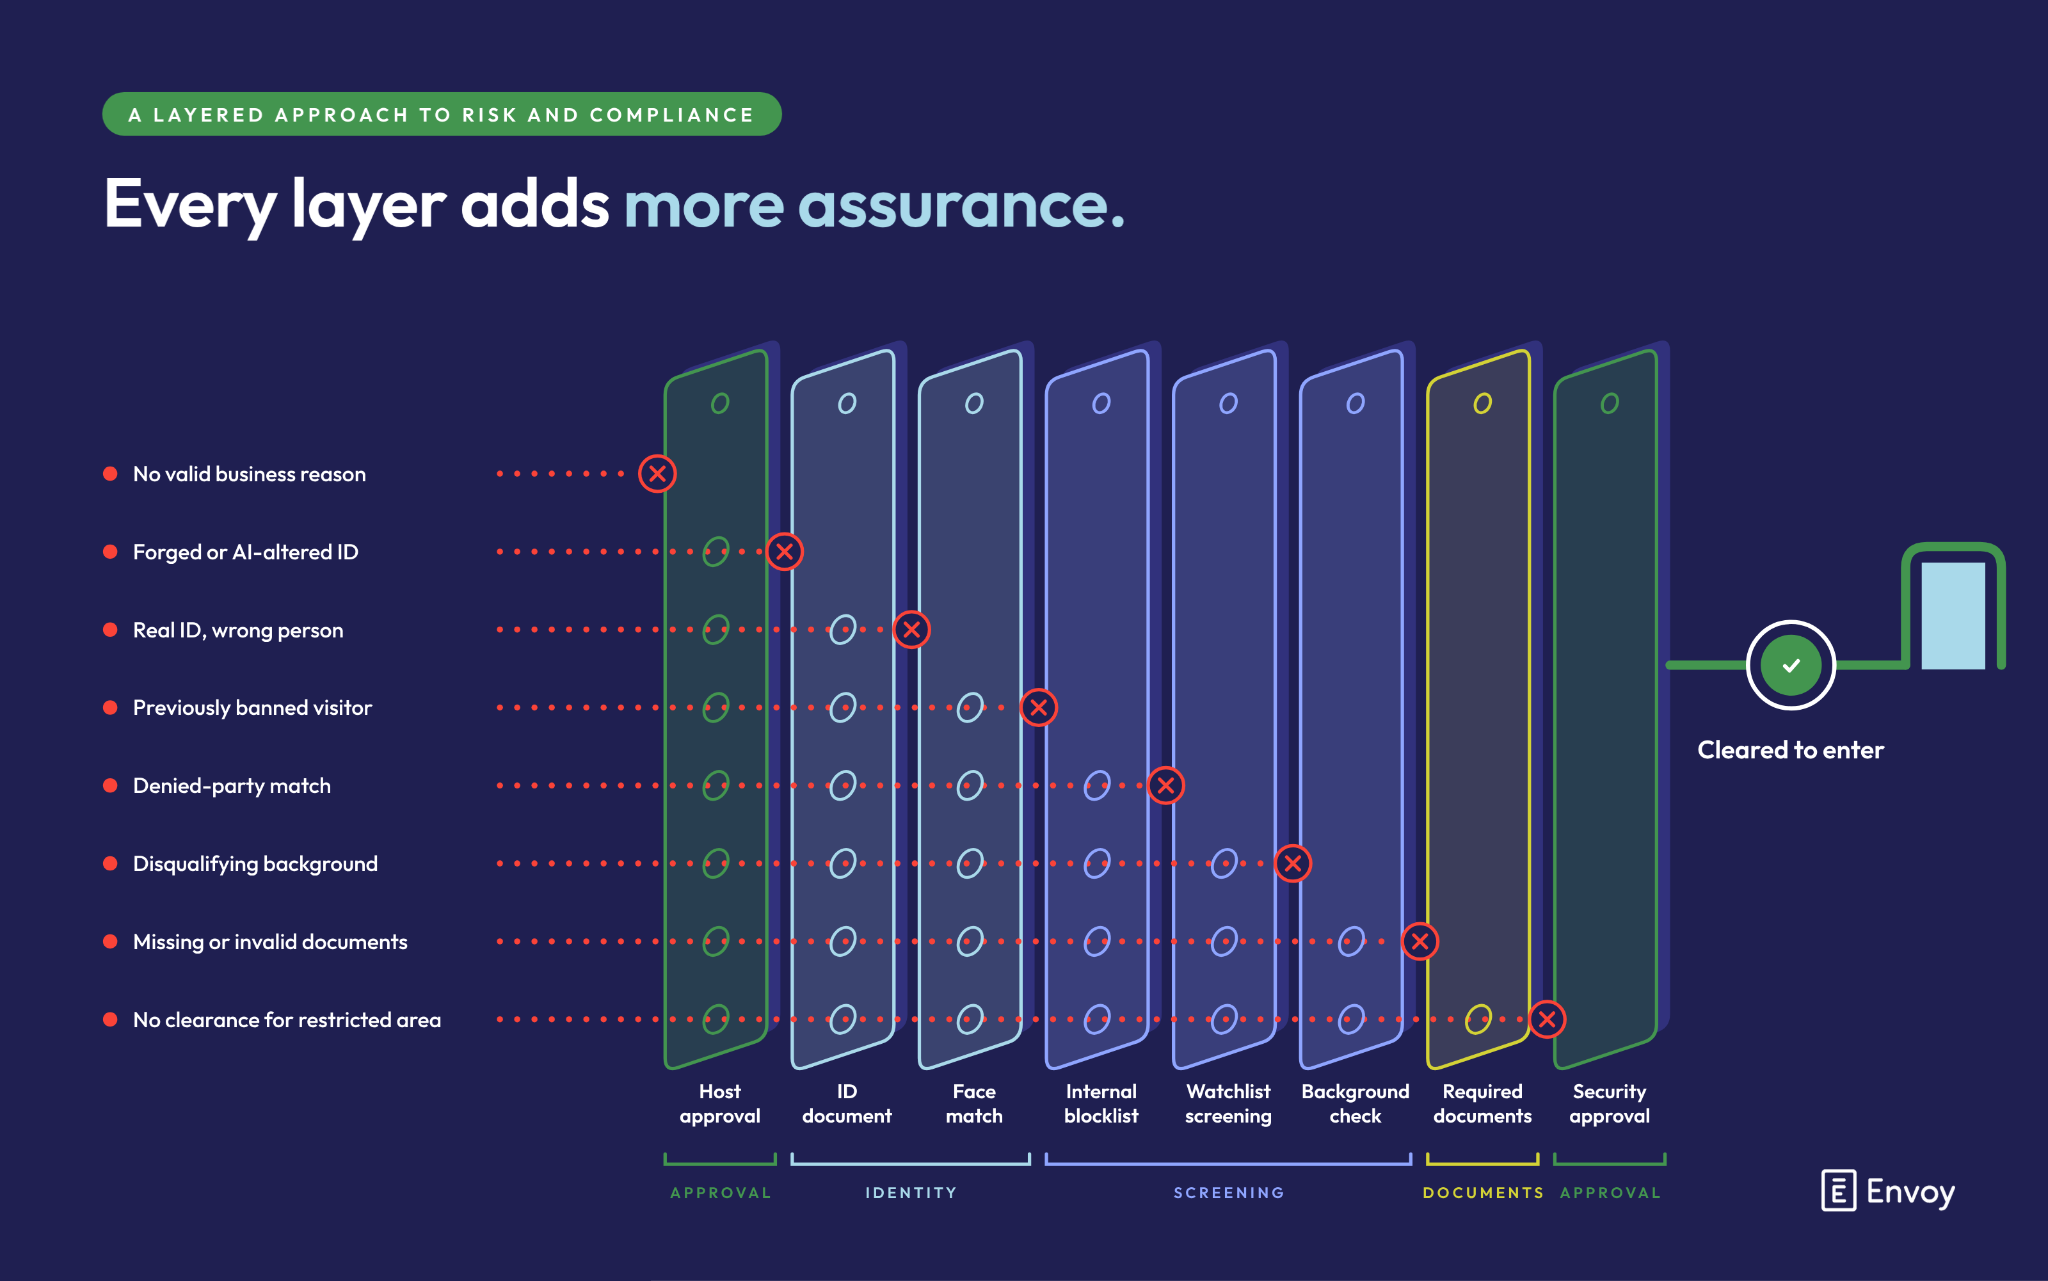
In critical environments, security is built in layers. Identity verification, watchlist screening, and human approvals each address risks the others may not detect. Because the threat landscape is constantly evolving, no single check should be treated as final. Visitors Critical allows each layer to be applied on an ongoing basis: identity can be re-verified at arrival, screening can be rerun between invitation and arrival, and approvals can require sign-off from multiple reviewers. Organizations can compose which layers apply, the stringency of each, and how often each runs, based on visitor type, facility, and risk level. For example, a vendor delivering catering and a foreign national touring an export-controlled lab each receive the level of scrutiny their risk requires.
Tailored to your industry
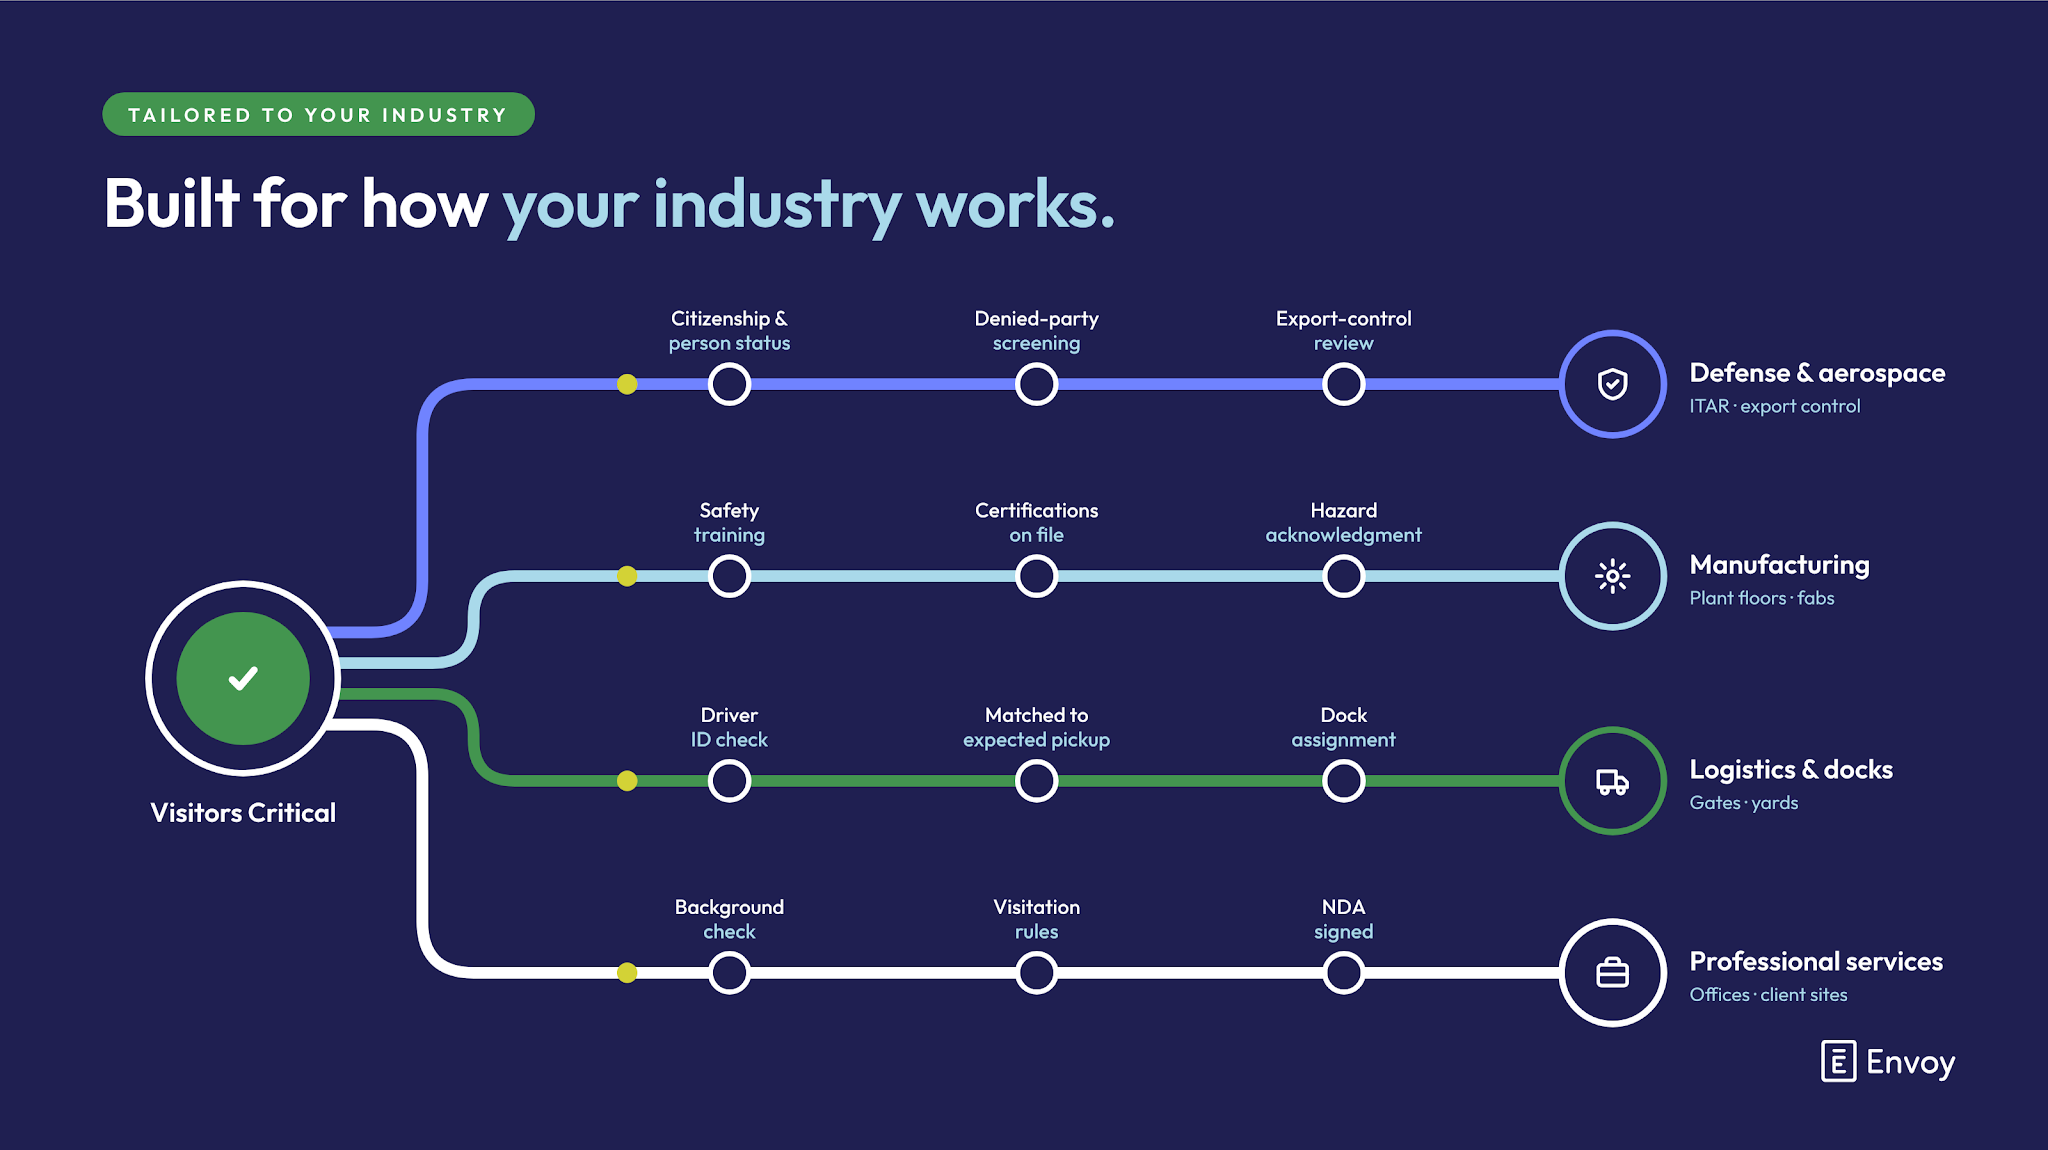
Different industries have their own security best practices and compliance frameworks that they check against. Citizenship and person status in defense and aerospace. Safety training and certifications on the manufacturing floor. Drivers verified against expected pickups at the dock. Visitation rules and business hours for services firms. With Approval Workflows, Visitors Critical covers them all with customizable forms, documents, and assessments, plus integrations with industry-specific screeners like MK Denial, Visual Compliance, Ontic, and Checkr, so every site runs the checks its risk profile requires.
Sensitive data should be need-to-know
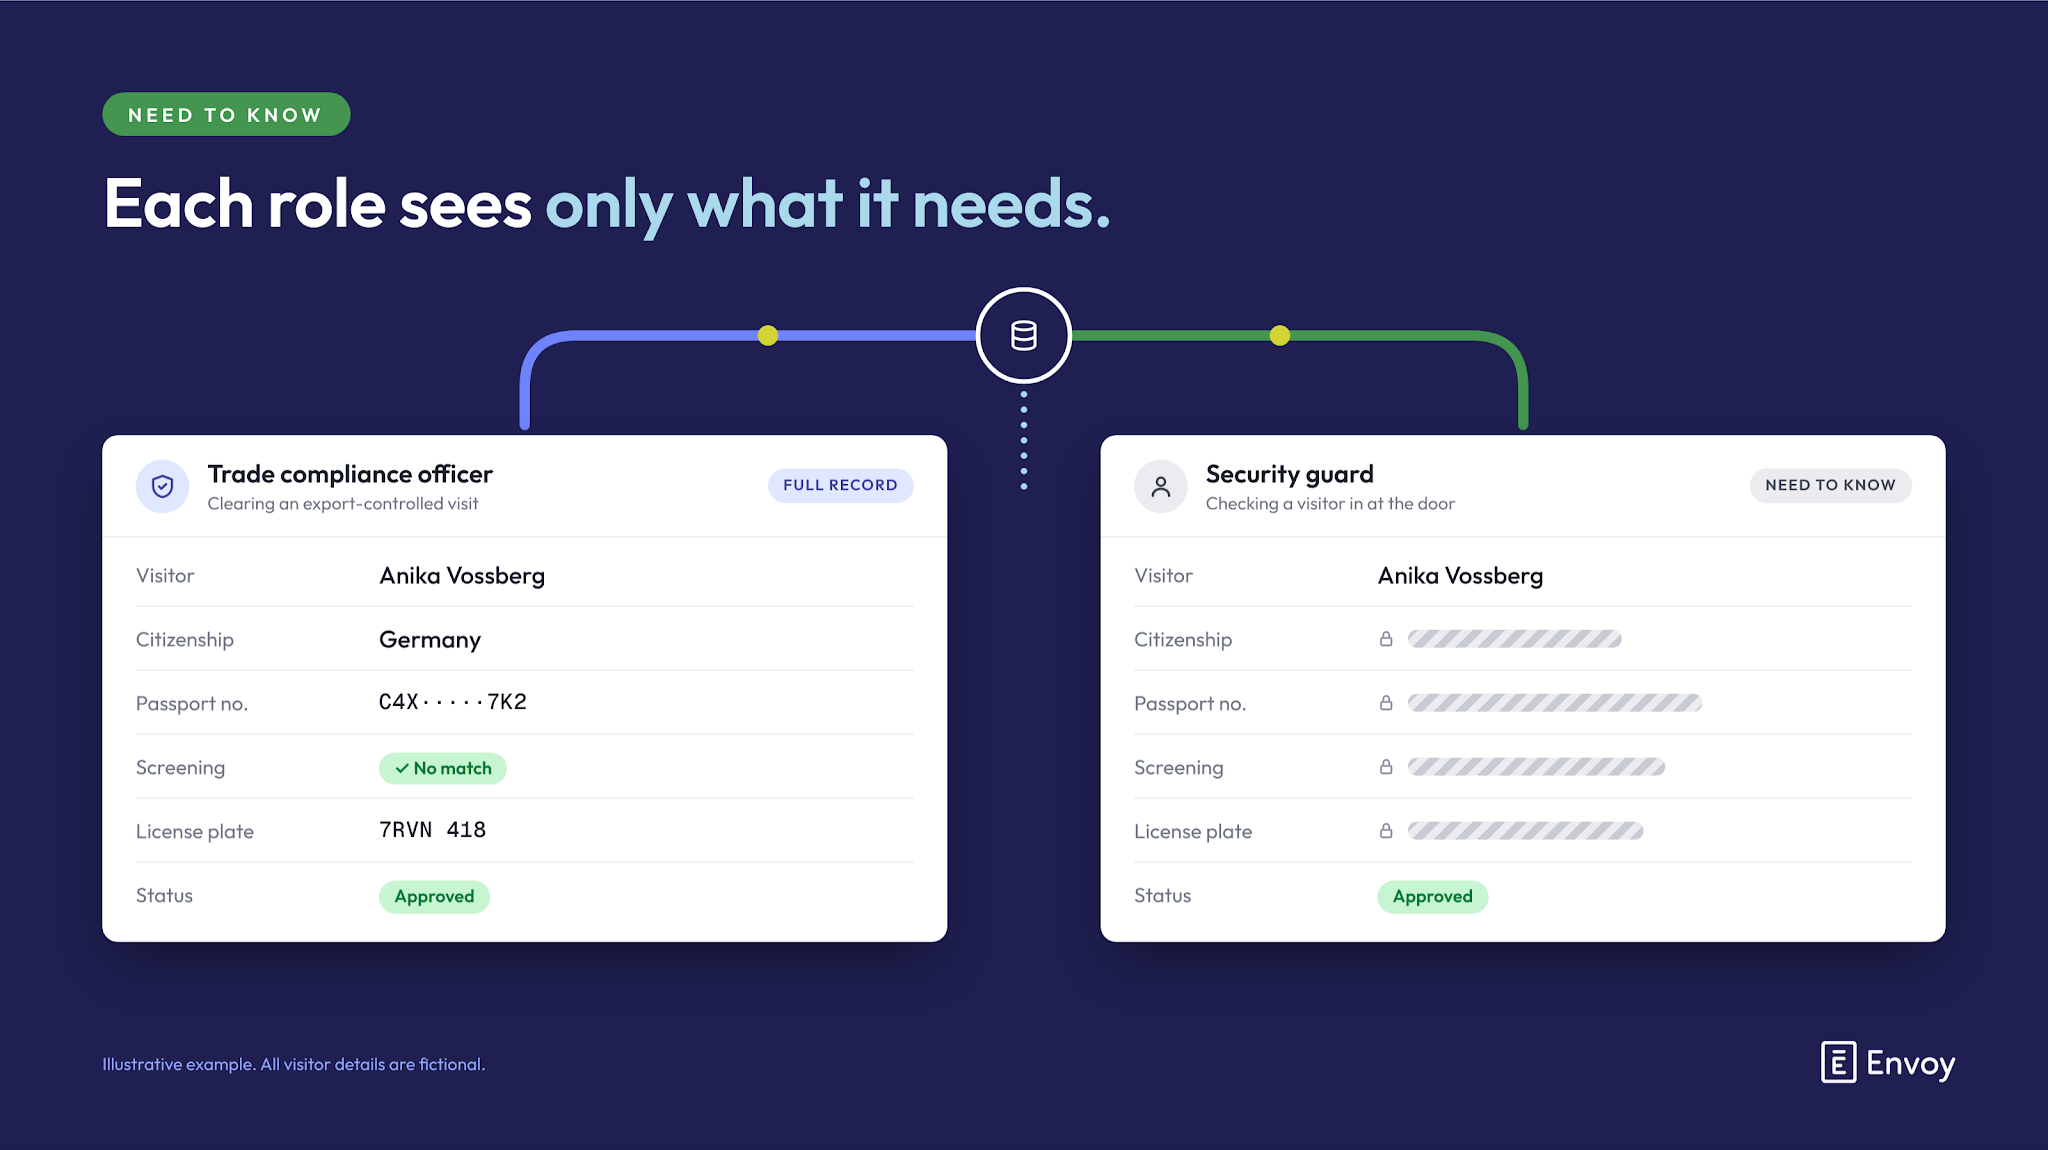
Protecting high-consequence environments requires collecting sensitive data, including identity documents, citizenship, and screening results. We built Visitors Critical on the principle your facilities already operate on: need to know. Visitors submit their information directly into the system, so sensitive documents never sit in inboxes or on paper forms. Once collected, access is partitioned by role: trade compliance sees passport numbers and citizenship, while a security guard sees only a name and an approval status. Configurable retention periods purge records once they are no longer needed, limiting exposure.
Ease of use drives adoption, and adoption is security
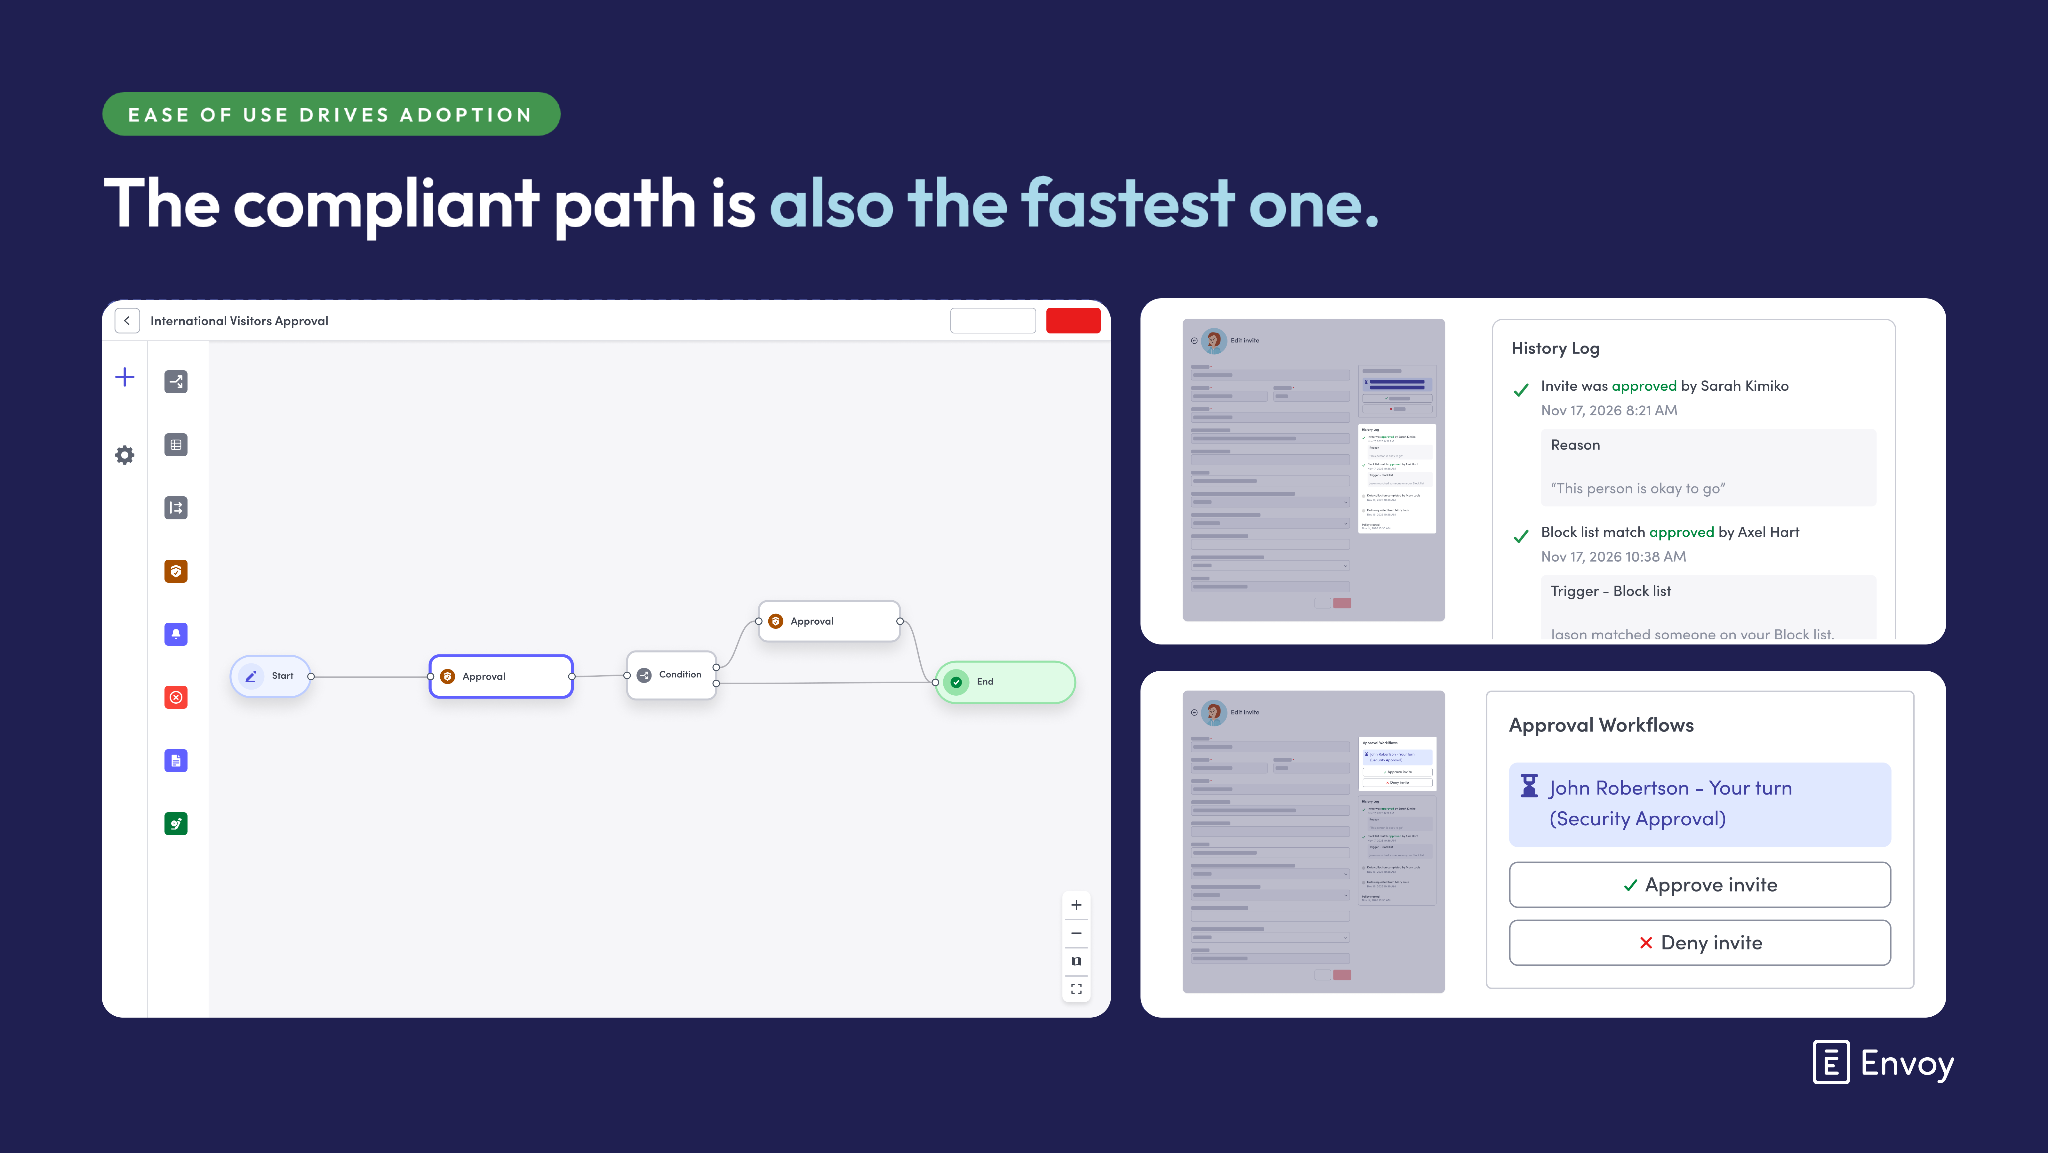
We believe that user experience is a security feature. When a system is slow or confusing, people route around it and the gaps come back. We designed Visitors Critical so the compliant path is also the fastest one: policies are set once and enforced at every site, a global blocklist is set by default, clear tasks and calls to action for approvers, transparent visibility into the state of a visit, and notifications that reach the right approvers in the tools they already use.
What’s next for Envoy?
In 2027, we’ll keep building Visitors Critical with the customers who need it most: helping close more security gaps, adding new layers of verification and assurance, expanding to more visitor types and complex sites, tightening data controls, and integrating more deeply with your security and safety technology stack.
Envoy started by replacing the antiquated paper logbook with a delightful check-in experience. With Visitors Critical, we are bringing that same thinking to critical environments. Experience and security are not competing priorities. A well-designed experience is what makes security effective.
“When a process is easy to follow, visitors complete it, hosts don’t work around it, and front desk teams enforce it consistently every time.”
Every visitor, whether a customer, auditor, prospective partner, or future hire, forms an impression of your organization at the door. They should feel welcome, and you should feel secure. Now you don’t have to choose.

Read more

In this blog post, we cover the basics of guest management: what it is, the top challenges associated with it, and how a VMS helps address these issues.

Tim Reed has secured facilities at Apple, Uber, and Aurora Innovation. Here's how he thinks about visitor management, and why most programs don't go far enough.
In this post, we’ll cover what a visitor policy is and walk through practical steps to create one that supports both security and compliance.

In this post, we go over the basics of what to look for when evaluating a visitor management system for your business.

Learn how a visitor management system can help you conquer compliance and be regulatory-ready in 2024 and beyond.
In this beginner's guide, we cover all the basics about visitor logs, including what they are, how they work, the info you should include, and more.