

Take control of sensitive visitor data
Visitor records hold names, photos, and ID scans. If too many people can see them, or you keep them too long, a privacy incident or a failed audit gets much more likely. Envoy lets you decide who sees sensitive details, set how long records are kept, and stay ready for audits.


We can collect all the data that we need to meet our compliance requirements in one, centralized place. We trust that Envoy protects that data, stores it securely, and does so globally. That’s a big win."
Protect visitor data at every step
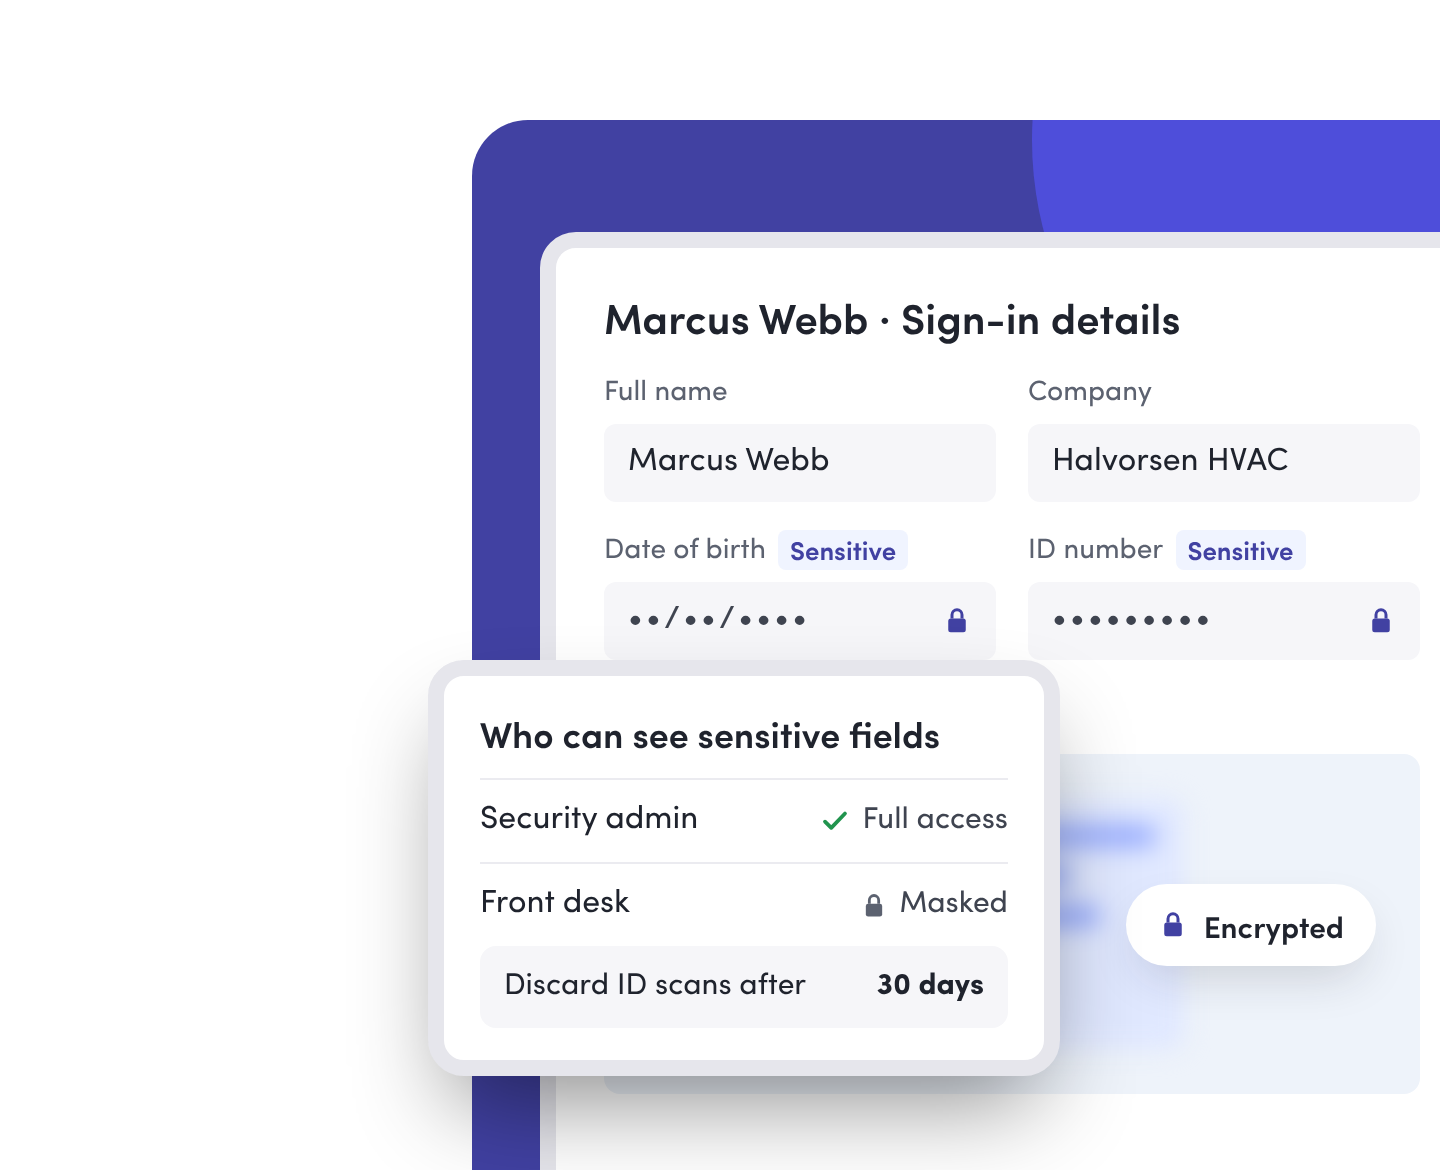
A contractor arrives at your front desk. They scan their ID, sign an NDA, and head to their meeting. Behind the scenes, Envoy encrypts the ID image, shows the front desk only what it needs to check them in, and limits the full record to the roles you approve. When the retention period ends, the details you chose are removed on schedule. That visit stays private from sign-in to cleanup.
Give each role the access it needs
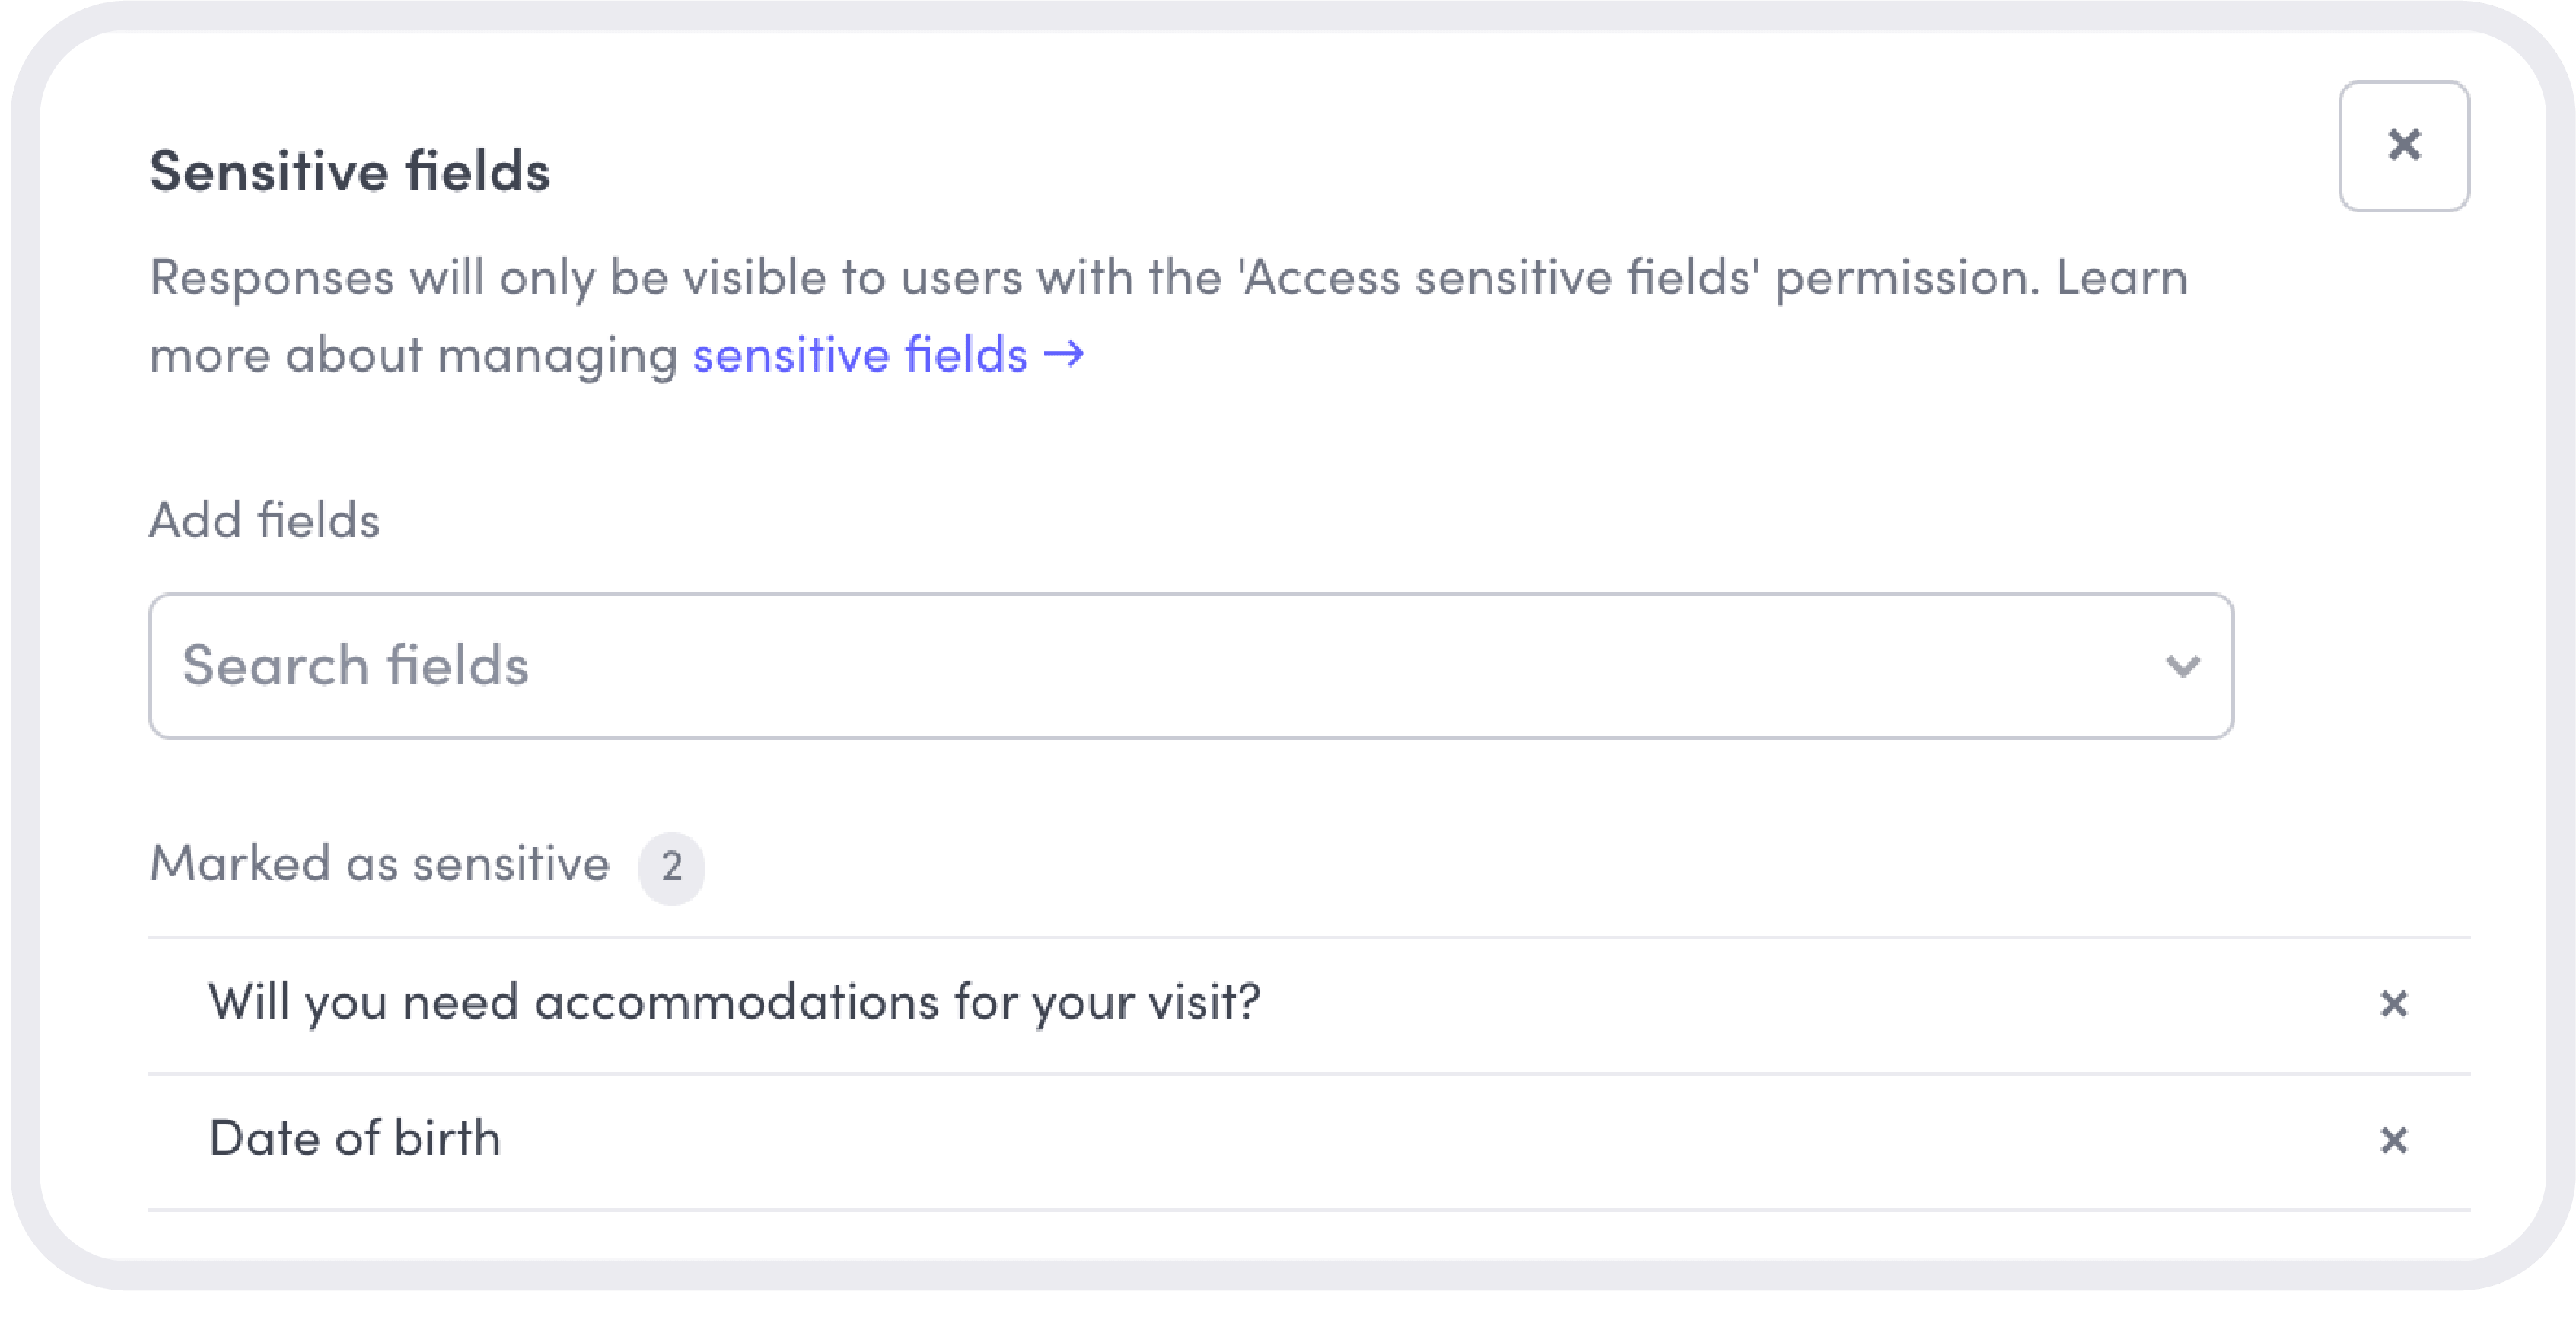
Different responsibilities call for different levels of visibility. Restrict who can view PII and sensitive visitor fields by role, giving authorized team members access to the details their work requires.
Make responsible data handling part of the visit

Explain what you collect
Display your organization’s data policy during sign-in so visitors can read how their information will be handled. Envoy also supports consent collection, with a configurable message directing visitors who decline consent to the next step.

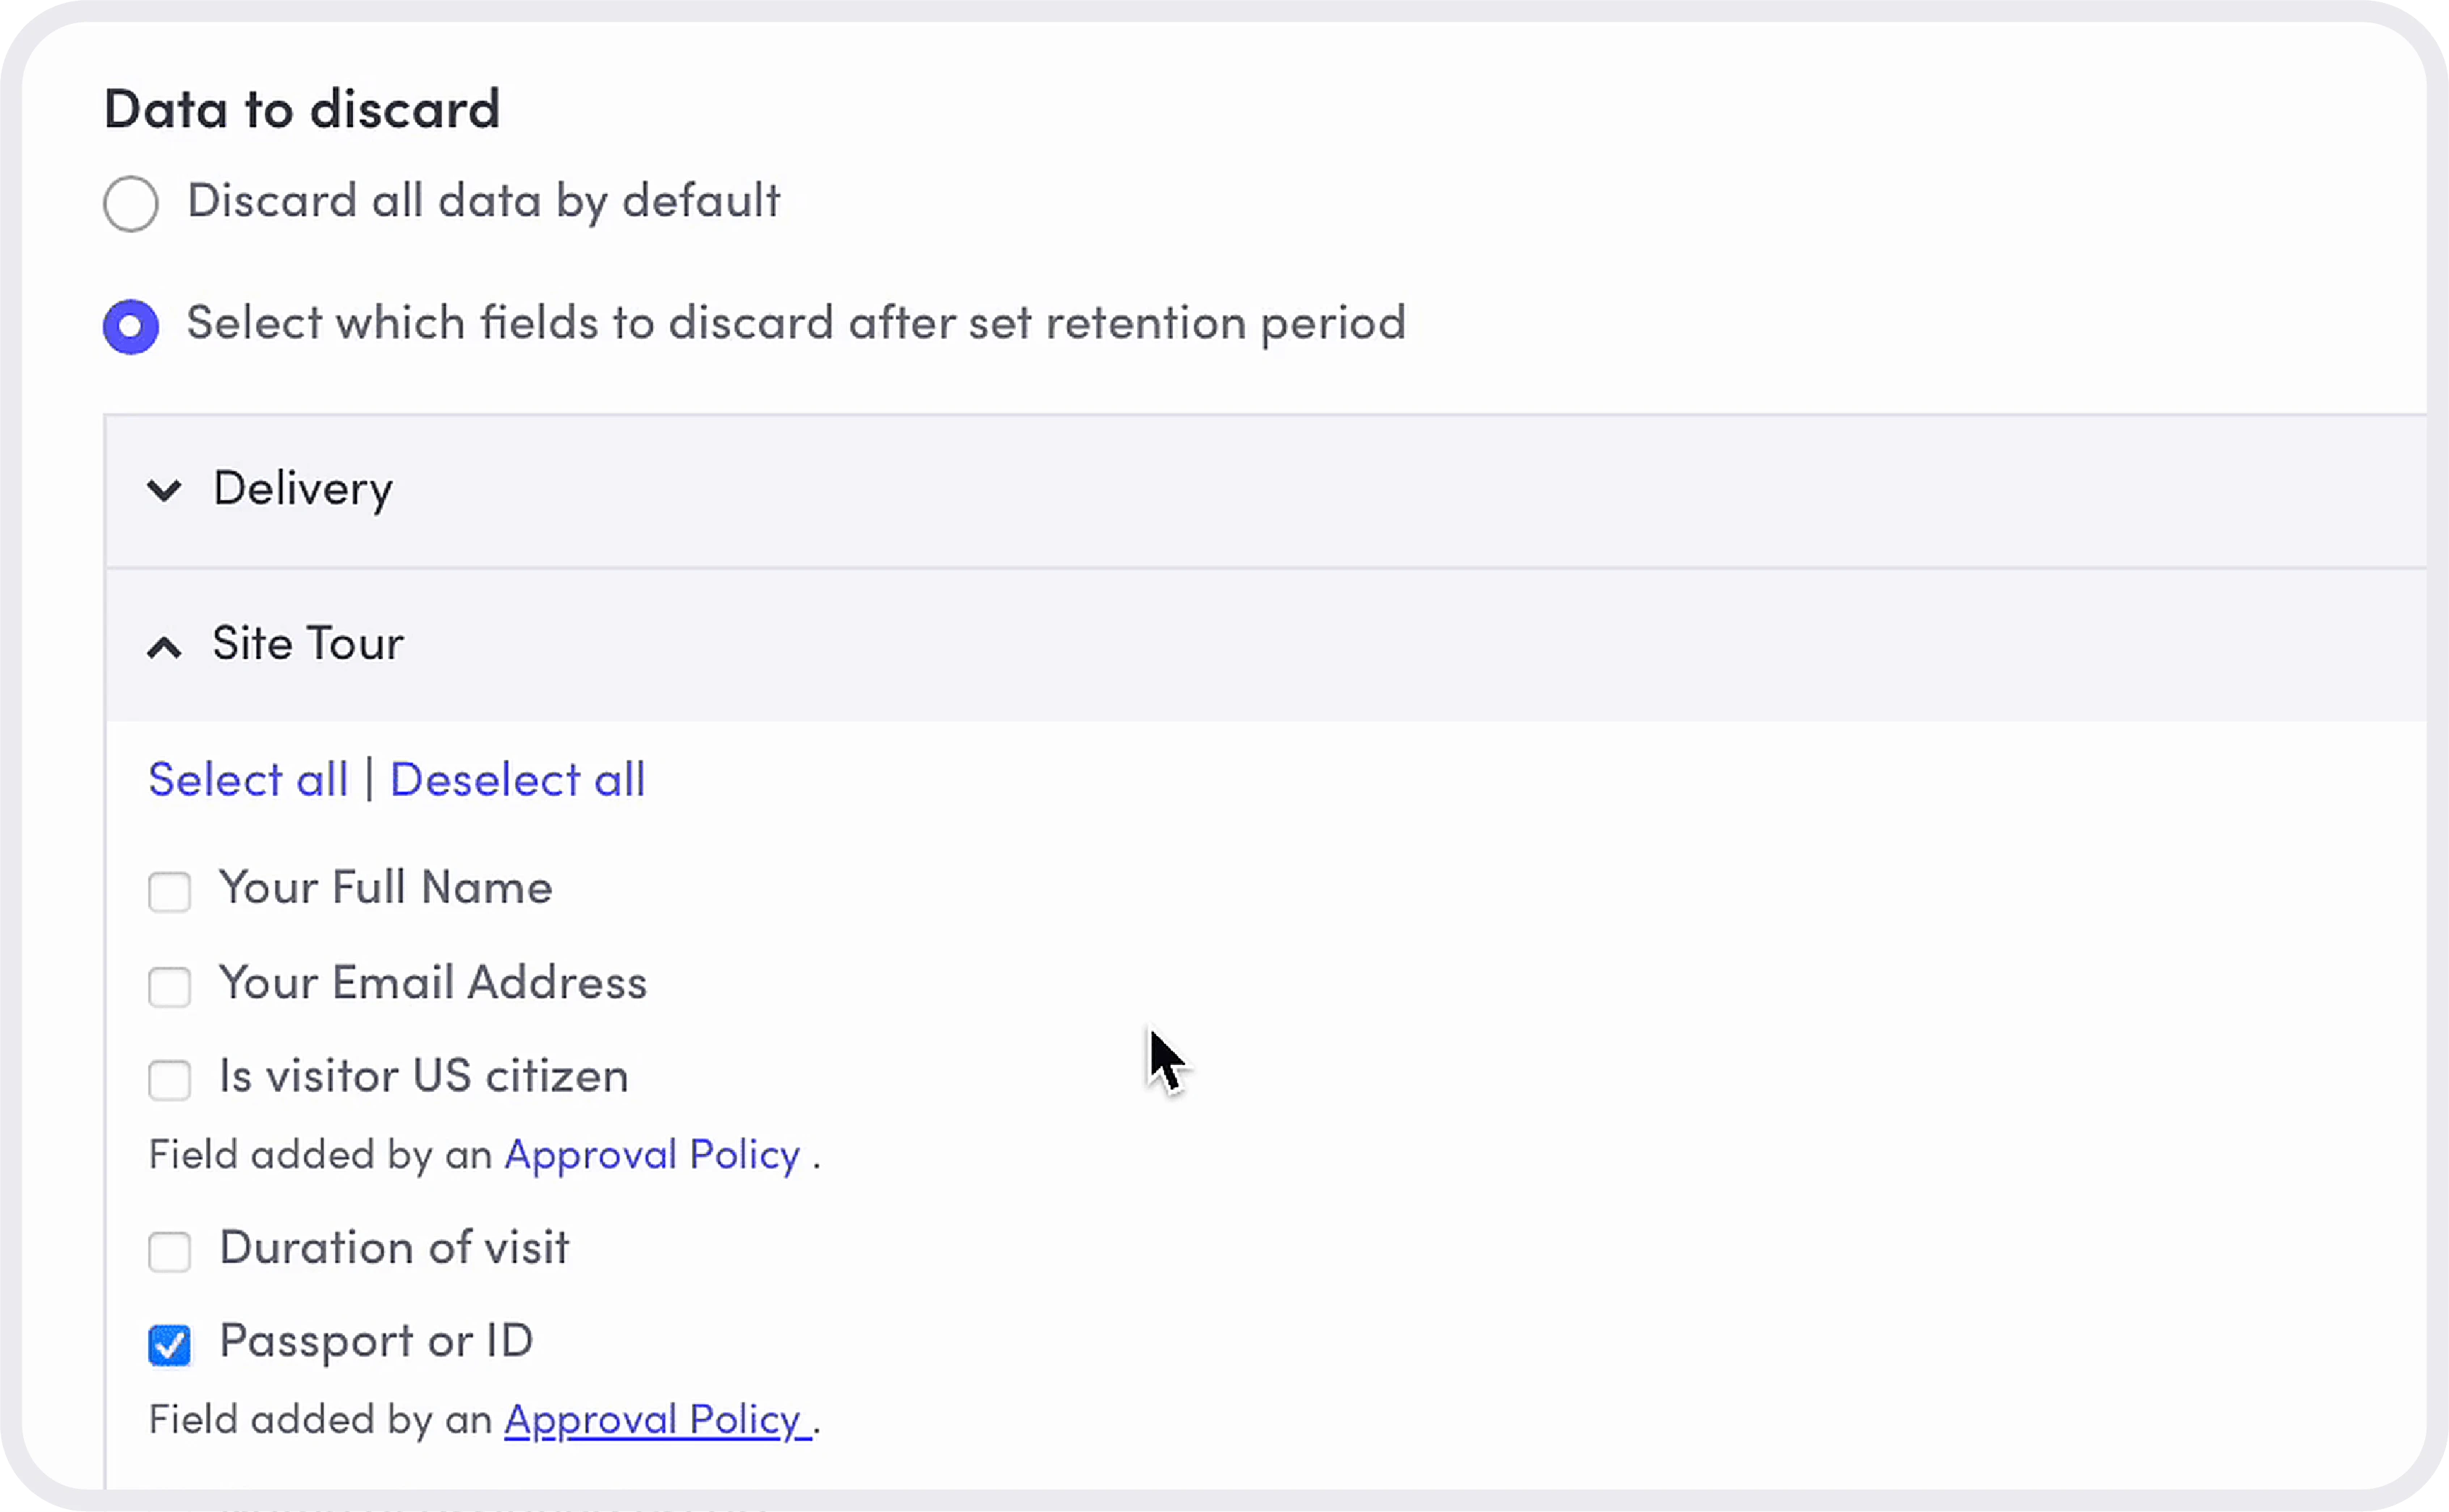
Set retention at the field level
Choose which sign-in fields and visitor files fall under your retention policy, including photos, signed legal documents, uploaded documents, and ID scans. Apply those selections to the visitor flows you use.

Standardize recurring reports
Save audit export templates for a location or share them across your organization. Reuse the fields, visitor types, date range, and format your team needs without rebuilding each report.

Export the details each review requires
Select the information relevant to a review and export it as a CSV or PDF. Your team can provide a specific set of visitor details instead of exporting the complete record.
Protect visitor information at every step
Identity checks, screening, and approvals bring sensitive information into your visitor process. Visitors Critical brings these controls together with sensitive data handling, so your team can manage visitor access and protect the information behind each decision.
Still have questions?
We can help.
Sensitive data handling lets you restrict who can view visitor PII and sensitive fields based on their role. Those restrictions apply across notifications and communication channels as well as the dashboard, helping your team control where personal details are visible.
Envoy is ISO/IEC 27001 certified and SOC 2 Type 2 audited. Visit our Trust Center to see how we support GDPR, CCPA, CPRA, and HIPAA, and to request security documentation.
They do. Envoy carries role-based visibility rules through notifications and communication channels, so receiving a notification doesn’t give someone access to fields their role isn’t authorized to view.
By default, visitor data is retained indefinitely while you remain an Envoy customer. Your team can configure a retention period and select which information to discard when that period ends. Information outside those selections remains stored.
The visit or invitation still counts in your analytics after personal information is removed. You can track how many people visited without keeping their personal details.
Envoy combines role-based visibility with retention settings, data policy disclosure, and consent options. These controls help your team apply its privacy policies and support obligations such as GDPR and CCPA. Your organization determines what information it needs to collect, who should see it, and how long it should be kept.
Envoy lets you save export selections as a template and use them again for later reviews. Templates can be available to one location or shared across your organization, with CSV and PDF export options.